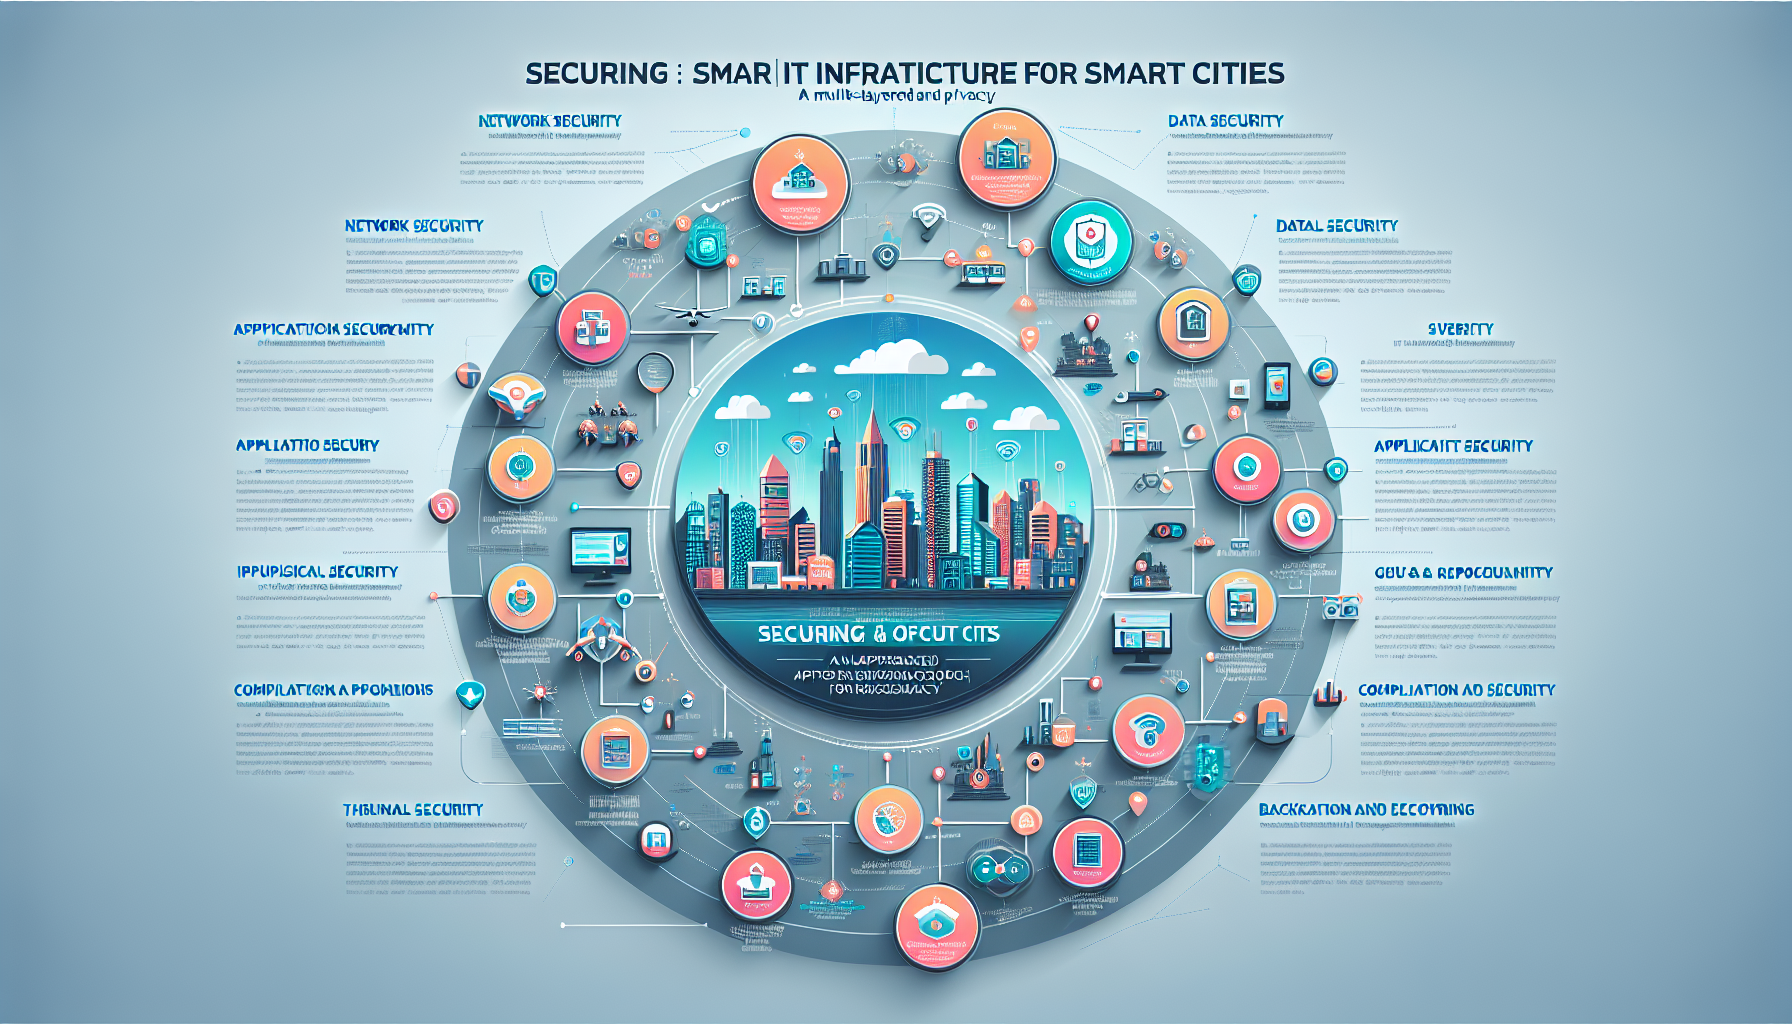
Smart city infrastructure connects everything — traffic sensors, water meters, public Wi-Fi, emergency services — so a single breach can cascade across physical systems. Here’s how to lock it down.
1. Network Security
Segment the network into isolated zones (IoT devices, public access, internal operations) to limit lateral movement.
Adopt Zero Trust: never trust, always verify. Every device, user, and application must authenticate and authorize before access.
Encrypt all data in transit and at rest with AES-256 and TLS 1.3.
Deploy next-gen firewalls and IDS/IPS to monitor and block malicious traffic.
Require VPNs for all remote access.
2. IoT Device Security
Change default passwords, disable unused services, and keep firmware current.
Enable secure boot so only signed firmware runs.
Run EDR on IoT gateways and endpoints to catch anomalous behavior.
Enforce mutual TLS authentication before any device joins the network.
3. Data Security
Classify data by sensitivity and define policies for collection, storage, access, and disposal.
Apply RBAC and least-privilege everywhere.
Mask or tokenize PII and other sensitive fields in non-production environments.
Back up critical data daily, test restores quarterly, and keep immutable copies off-site for ransomware recovery.
4. Application Security
Bake security into every SDLC phase — threat modeling, SAST/DAST, dependency scanning.
Patch applications and libraries within your SLA window; automate where possible.
Put WAFs in front of public APIs and web apps to stop injection and XSS.
Run internal and third-party pen tests at least annually and after major changes.
5. Physical Security
Control data-center access with biometrics, RFID badges, and video surveillance.
Monitor temperature, humidity, and power in real time; alert on deviations.
Run UPS and generator backup with automatic failover tested monthly.
6. Cloud and Virtualization Security
Enforce MFA for all cloud console and API access.
Secure API gateways with rate limiting, schema validation, and audit logging.
Ali YAZICI is a Senior IT Infrastructure Manager with 15+ years of enterprise experience. While a recognized expert in datacenter architecture, multi-cloud environments, storage, and advanced data protection and Commvault automation , his current focus is on next-generation datacenter technologies, including NVIDIA GPU architecture, high-performance server virtualization, and implementing AI-driven tools. He shares his practical, hands-on experience and combination of his personal field notes and “Expert-Driven AI.” he use AI tools as an assistant to structure drafts, which he then heavily edit, fact-check, and infuse with my own practical experience, original screenshots , and “in-the-trenches” insights that only a human expert can provide.