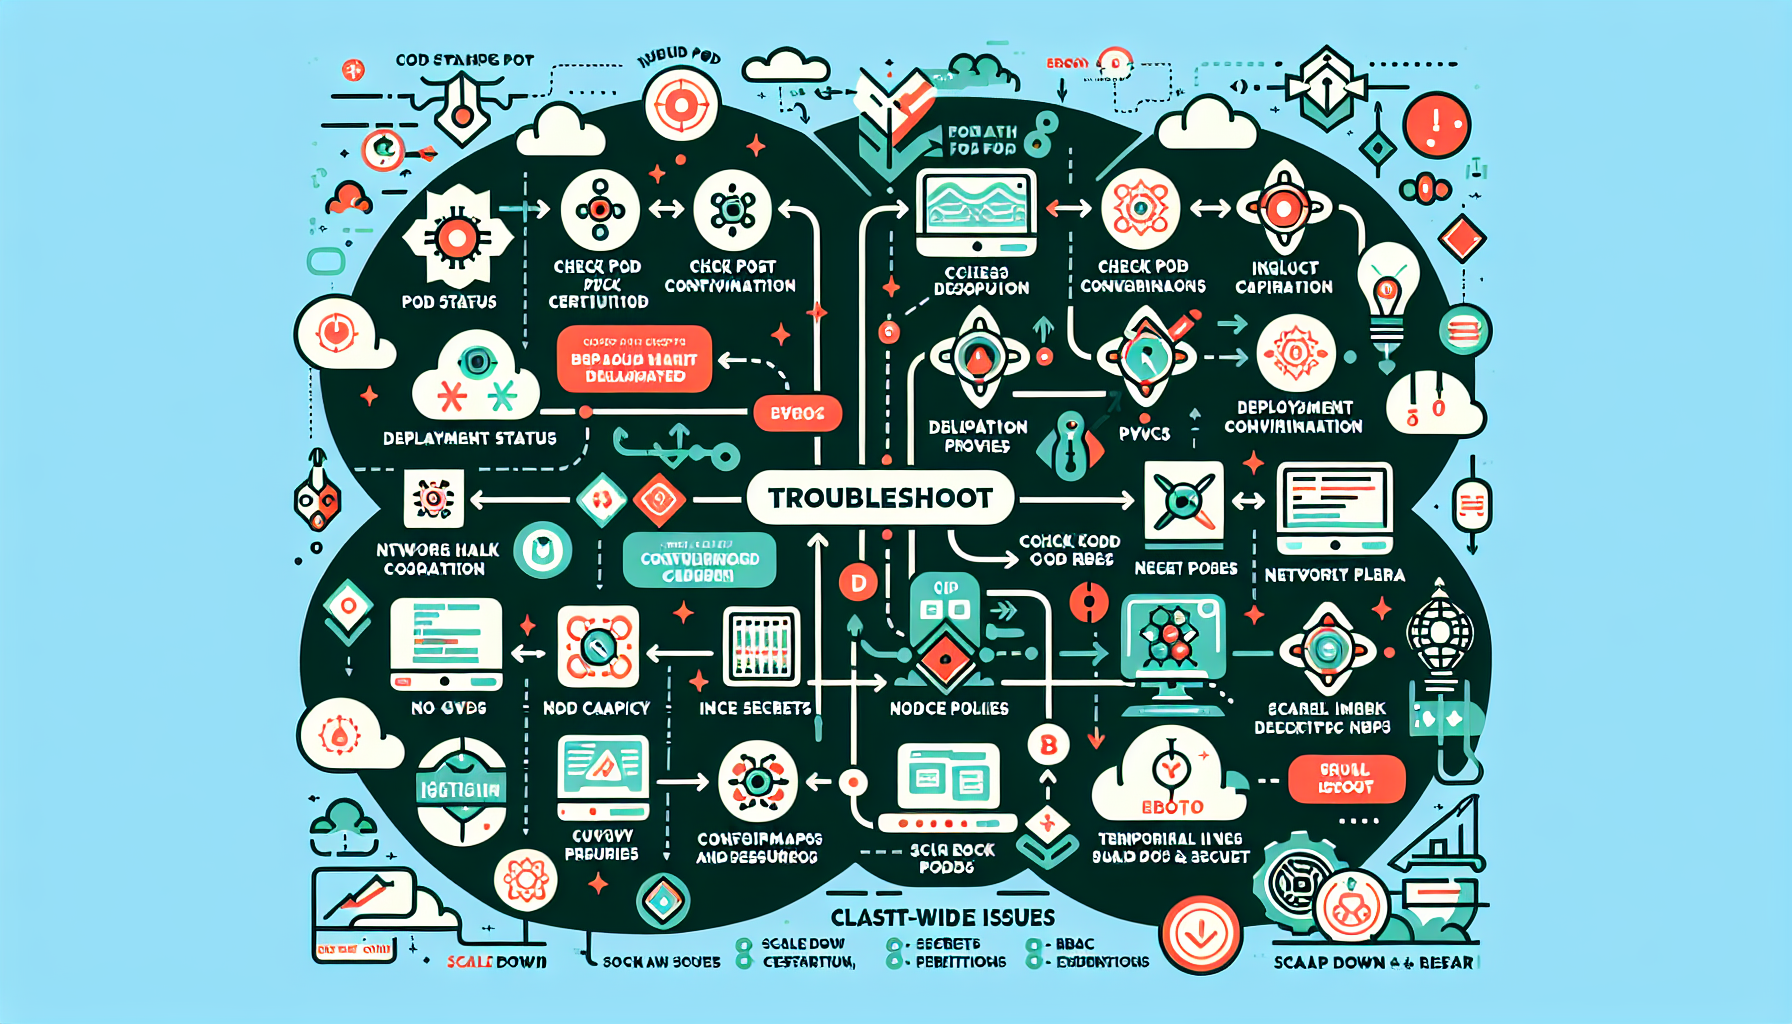
If the pod uses storage, verify the PVCs: bash
kubectl get pvc -n <namespace>
kubectl describe pvc <pvc-name> -n <namespace>
Typical issues:
PVC not bound to a Persistent Volume (PV).
Storage class misconfiguration.
Insufficient storage capacity.
7. Check Image Configuration
Verify the container image is correct and accessible:
Confirm the image name and tag are correct.
Ensure the image exists in the container registry.
If the image is private, confirm the proper image pull secret is configured: bash
kubectl get secret -n <namespace>
8. Inspect Network Policies
If the pod relies on network communication, verify NetworkPolicies aren’t blocking traffic: bash
kubectl get networkpolicy -n <namespace>
Ensure required ports and communication paths are allowed.
9. Examine Pod Health Probes
Check readiness and liveness probes in the deployment configuration: yaml
livenessProbe:
httpGet:
path: /healthz
port: 8080
readinessProbe:
httpGet:
path: /ready
port: 8080
Misconfigured probes cause pods to restart or fail to become ready.
10. Validate ConfigMaps and Secrets
Ensure ConfigMaps and Secrets referenced in the pod are correctly defined: bash
kubectl get configmap -n <namespace>
kubectl get secret -n <namespace>
Verify the pod has permissions to access them.
11. Check Cluster-Wide Issues
Investigate cluster-wide issues affecting pod deployment:
Review key component status: bash
kubectl get nodes
kubectl get --raw='/readyz?verbose'
Check for resource constraints or node failures.
12. Debug with Temporary Pods
Spin up a temporary pod to inspect the environment: bash
kubectl run debug-pod --rm -i --tty --image=nicolaka/netshoot -- sh
Use busybox if you only need basic shell tools.
13. Review Kubernetes Logs
Examine kubelet or control plane logs for scheduling or runtime errors.
On the node, check kubelet logs directly.
Use your monitoring/logging stack (ELK, Prometheus, Grafana, Loki) for deeper investigation.
14. Scale Down and Restart
If the deployment has multiple replicas, try scaling to zero and back up: bash
kubectl scale deployment <deployment-name> --replicas=0 -n <namespace>
kubectl scale deployment <deployment-name> --replicas=<desired-number> -n <namespace>
Note: this causes downtime. Use kubectl rollout restart for zero-downtime restarts.
kubectl port-forward to test application endpoints locally: bash
kubectl port-forward <pod-name> <local-port>:<container-port> -n <namespace>
16. Review RBAC and Permissions
Ensure the pod has necessary permissions if it interacts with the API or other cluster resources: bash
kubectl auth can-i <verb> <resource> --as=<service-account>
17. Consult Logs from External Systems
If the pod interacts with external systems (databases, APIs), check for connectivity and authentication issues.
Ali YAZICI is a Senior IT Infrastructure Manager with 15+ years of enterprise experience. While a recognized expert in datacenter architecture, multi-cloud environments, storage, and advanced data protection and Commvault automation , his current focus is on next-generation datacenter technologies, including NVIDIA GPU architecture, high-performance server virtualization, and implementing AI-driven tools. He shares his practical, hands-on experience and combination of his personal field notes and “Expert-Driven AI.” he use AI tools as an assistant to structure drafts, which he then heavily edit, fact-check, and infuse with my own practical experience, original screenshots , and “in-the-trenches” insights that only a human expert can provide.